For years, digital privacy was a battle fought entirely inside your web browser. Advertisers used third-party cookies to track you, and privacy advocates responded by building tools to block those specific files. Recently, major browsers like Safari and Firefox completely banned third-party cookies by default, successfully cutting off the primary surveillance pipeline.
However, the advertising technology (AdTech) industry did not simply accept defeat. Instead, they escalated the conflict. If browsers are going to block third-party trackers, the data brokers have decided to stop acting like third parties. Using a highly deceptive technique known as CNAME Cloaking, surveillance networks are now manipulating the fundamental routing infrastructure of the internet to disguise themselves as the very websites you trust.
What is CNAME Cloaking?
To understand this exploit, you have to look at how the Domain Name System (DNS) operates. DNS is the phonebook of the internet, translating human-readable URLs (like yourbank.com) into machine-readable IP addresses.
A CNAME (Canonical Name) is a specific type of DNS record. It functions exactly like a mail forwarding address. A website owner can use a CNAME to tell your browser, "If you are looking for subdomain.website.com, go look at other-website.com instead."
Data brokers have weaponized this simple routing feature to execute a massive digital masquerade. Here is how the deception works in real time:
- You log into a trusted website, like your primary banking portal.
- The bank's website attempts to load a tracking script from metrics.yourbank.com.
- Because the domain matches the bank you are visiting, your browser completely trusts the request.
- Behind the scenes, the bank's DNS server uses a CNAME record to secretly forward that request to evil-tracker-network.com.
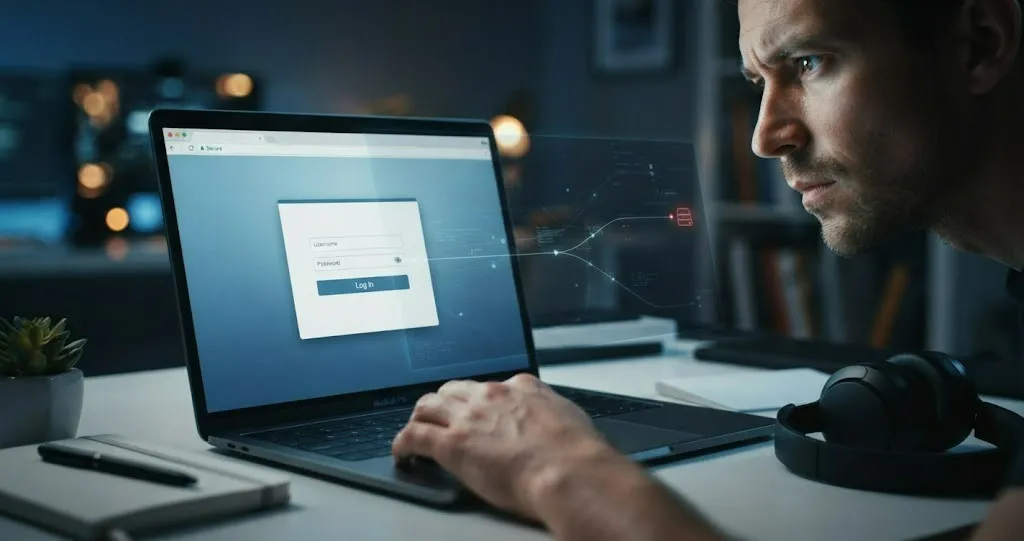
The tracker successfully extracts your behavioral data while wearing the trusted mask of your bank.
The first-party illusion and cookie leakage
The true danger of CNAME cloaking goes far beyond basic behavioral profiling. It represents a catastrophic vulnerability for your most sensitive personal data.
Because the hidden tracker is operating under a "first-party" subdomain, your web browser grants it absolute, unrestricted access. When you log into a website, the site issues you a secure "session cookie" — a cryptographic file that proves you are authenticated. This cookie is what keeps you logged in as you click from your account dashboard to your billing statements.
Standard web security protocols dictate that your browser must never send a first-party session cookie to a third-party server. But because CNAME cloaking tricks your browser into believing the tracker is actually the bank, your browser voluntarily hands over your secure, authenticated session cookie directly to the AdTech company.
The tracker does not have to hack your connection to steal your login session; the DNS manipulation tricks your browser into handing the keys over directly.
Why legacy blockers are blind
Attempting to stop this surveillance with legacy privacy extensions is fundamentally impossible due to how web architecture works.
| Legacy defense | What it checks | Why it fails |
|---|---|---|
| Apple ITP / Mozilla ETP | Blocks third-party cookies | CNAME cloaking operates entirely as a first-party request, so these built-in defenses view the tracker as a safe component and wave it right through |
| Traditional ad blocker | The URL your browser asks for (metrics.yourbank.com) | It has no visibility into the DNS routing layer, so its blocklist of known tracker domains is rendered completely useless |
The pattern is the same as in earlier articles in this series: these tools are not broken. They simply guard a surface the deception no longer passes through.
Unmask the trackers with Total Adblock
Protecting your secure session data from subdomain deception requires a defense system that can look past the URL in your address bar and interrogate the actual DNS routing infrastructure. You cannot trust the browser's surface-level security when the deception is happening at the network layer.
Total Adblock is specifically engineered to neutralize CNAME cloaking. By utilizing advanced dynamic DNS uncloaking, Total Adblock does not just check the name of the link; it actively traces the CNAME routing path before the connection is established. It looks past the fake first-party mask (metrics.yourbank.com) and identifies the true, hidden destination (evil-tracker-network.com). Once the hidden surveillance network is exposed, Total Adblock forcefully severs the connection, ensuring your behavioral data and secure session cookies remain locked safely inside your browser.
Secure your digital perimeter today
You do not have to accept an internet where data brokers manipulate the core routing of the web to masquerade as the websites you trust. Upgrading your digital defense is the single most powerful step you can take to neutralize CNAME cloaking, stop the leakage of your secure session cookies, and enforce true isolation between your trusted accounts and third-party surveillance.
Total Adblock provides a highly automated solution that unmasks hidden trackers without breaking the legitimate websites you rely on. Stop letting data brokers hijack your DNS. Take back control of your digital workspace by making the switch to Total Adblock today.